A company receives two pentest proposals for its customer portal. The first costs less and promises a report in ten days. The second covers the portal, the API used by the mobile app, and a retest. Before comparing price and timeline, procurement and security need to answer the same question: do both proposals cover the same risk?
Define scope in terms vendors can price
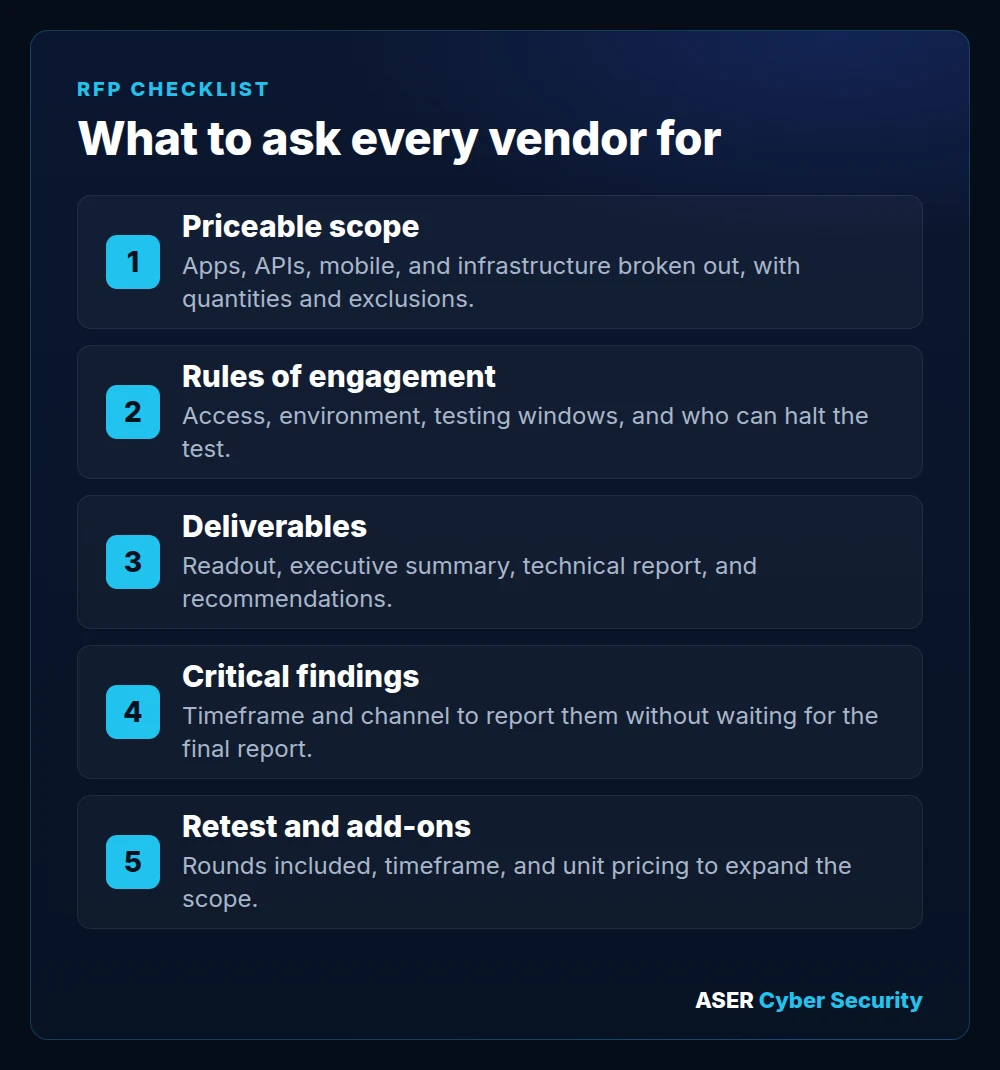
Start with the decision the test is meant to support. If the goal is to launch a new digital customer journey, specify which applications and integrations are part of it. List quantities, environments, user roles in scope, and exclusions. Break out, for example, the web portal, APIs, mobile app, and infrastructure, and describe the expected coverage for each workstream instead of simply asking for a “full pentest.”
Also document the dependencies: who provides authorized access, which environment the work can take place in, what the testing windows are, and who can halt the activity if it causes an impact. Assets operated by third parties stay out of scope until there is explicit authorization. The NIST SP 800-115 publication is a useful reference for defining these rules of engagement.
Compare what will be delivered and what could change the price
Ask every vendor to fill out the same table: workstream, assets and roles covered, assumptions, exclusions, timeline, price, and retest. Specify whether the price includes a readout meeting, an executive summary, a technical report with protected evidence, and remediation recommendations. Also ask for the timeframe and channel for reporting a critical finding without waiting for the final report.
For the retest, spell out how many rounds are included, how long you have to request them, and whether they cover only fixes to the original findings or later changes as well. If there are additional charges, ask for the unit price and the process for approving a scope expansion.
A sample comparison
Picture a retail chain with an ordering portal and two in-house APIs. Vendor A quotes the portal and one API; Vendor B covers both APIs and includes a retest. The difference in scope only becomes visible when each item is listed separately. The team can ask Vendor A to price the second API and the retest, and only then evaluate total cost, timeline, and quality of delivery.
In practice, the best question to ask before approving a proposal is: after the report and the retest, will we have enough evidence to decide what to fix and what has already been validated?
Template: pentest proposal comparison
| Workstream | Assets and roles | Assumptions and exclusions | Deliverables | Timeline and retest | Price and add-ons |
|---|---|---|---|---|---|
| Web portal | |||||
| API | |||||
| Mobile app |
At ASER, every Penetration Testing proposal breaks out workstreams, deliverables, and retest terms, including for e-commerce, mobile apps and networks. Request a proposal.