Brazil's C6 Bank fell victim to fraudulent diversions that caused losses of R$ 23 million. Here's what made it possible.
The São Paulo Civil Police are investigating the R$ 23 million fraud carried out by five thousand C6 Bank customers.
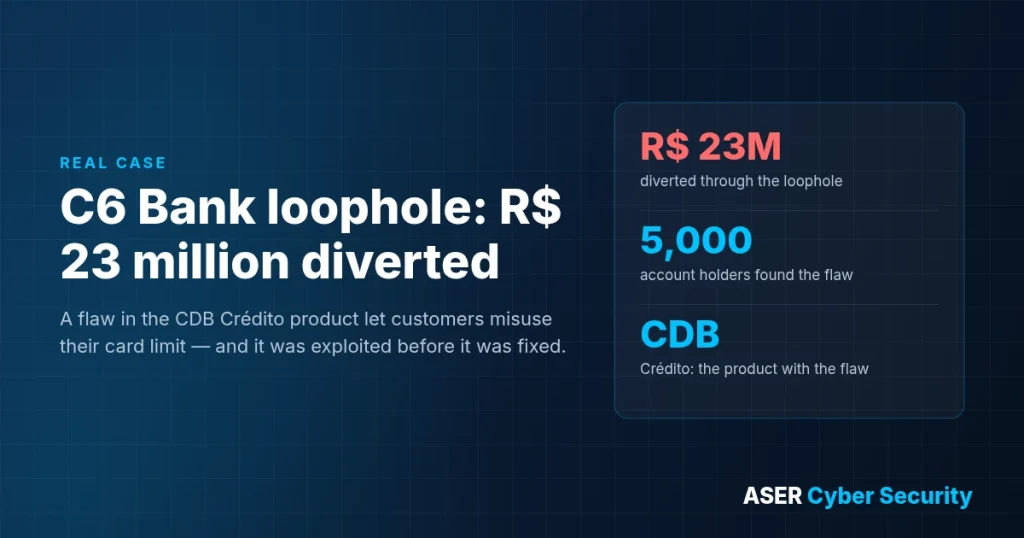
According to information published by Brazilian magazine Veja, the fraud took place in the fintech's CDB Crédito product, through a loophole that allowed customers to use the full credit limit granted in that product while also withdrawing the money they had invested.
CDB Crédito is a credit product the fintech offers through its credit card, in which the customer receives a credit limit equal to the amount invested in one of the institution's CDBs (Certificados de Depósito Bancário, Brazil's bank certificates of deposit).
What caused this loophole in the system?
The loophole, discovered by five thousand of the bank's account holders, allowed them to use the CDB Crédito card limit while also withdrawing the invested amount before it was locked as collateral for the credit.
In other words, slow systems and incorrect system rules created a loophole that let people take advantage and use these funds however they wanted.
In total, R$ 23 million was diverted through this loophole.
All because of a small loophole that could have been caught before the product was released to the public.
This is not the fintech's first financial loss: last year, it was hit by a scheme that led to the diversion of R$ 50 million.
You need to avoid flaws and loopholes like the one at the fintech.
This shows every business owner how important it is to check systems and apps for flaws and vulnerabilities.
But…
How can you identify loopholes in a system?
There is no way to identify vulnerabilities and system flaws without a thorough assessment.
That's why we believe every system should undergo ongoing vulnerability assessments.
A vulnerability assessment consists of identifying and classifying security gaps that can put your data infrastructure at risk.
???? This loophole could have been found sooner. The ASER Vulnerability Management identifies and classifies the flaws in your systems on an ongoing basis.
Some flaws are more common than others, such as:
- Programming and development errors;
- Misconfiguration of security tools such as the firewall;
- Lack of user access control;
- No security policy;
- Lack of specialized partners;
- Low investment in security;
It's worth noting that as a company's IT management maturity grows, it tends to become able to carry out these assessments on its own, with an in-house team.
But the best solution is still to hire a specialized team for this work.
How can you use a system assessment to fix loopholes?
Once the assessment is done and the data and errors have been gathered, you need to start applying the fixes.
The best way to make these fixes is to hire specialists in vulnerability assessment and remediation for the job.
Another way is to train people already at your company for this work, which will demand a lot of money and time.
Time is money, so take this opportunity to fix your flaws now.
To assess and fix your system vulnerabilities, count on Aser Security. We have top digital security experts ready to help you improve your security.
Talk to one of our consultants to learn about the vulnerability assessment services we offer.
How many loopholes are in your systems right now?
For more than 20 years, ASER has protected Brazilian companies with 100% managed security. Talk to an expert and get a free assessment of your business risks.